ENGW-201 / ENGW-209 — Admin Authentication Flow (FE)
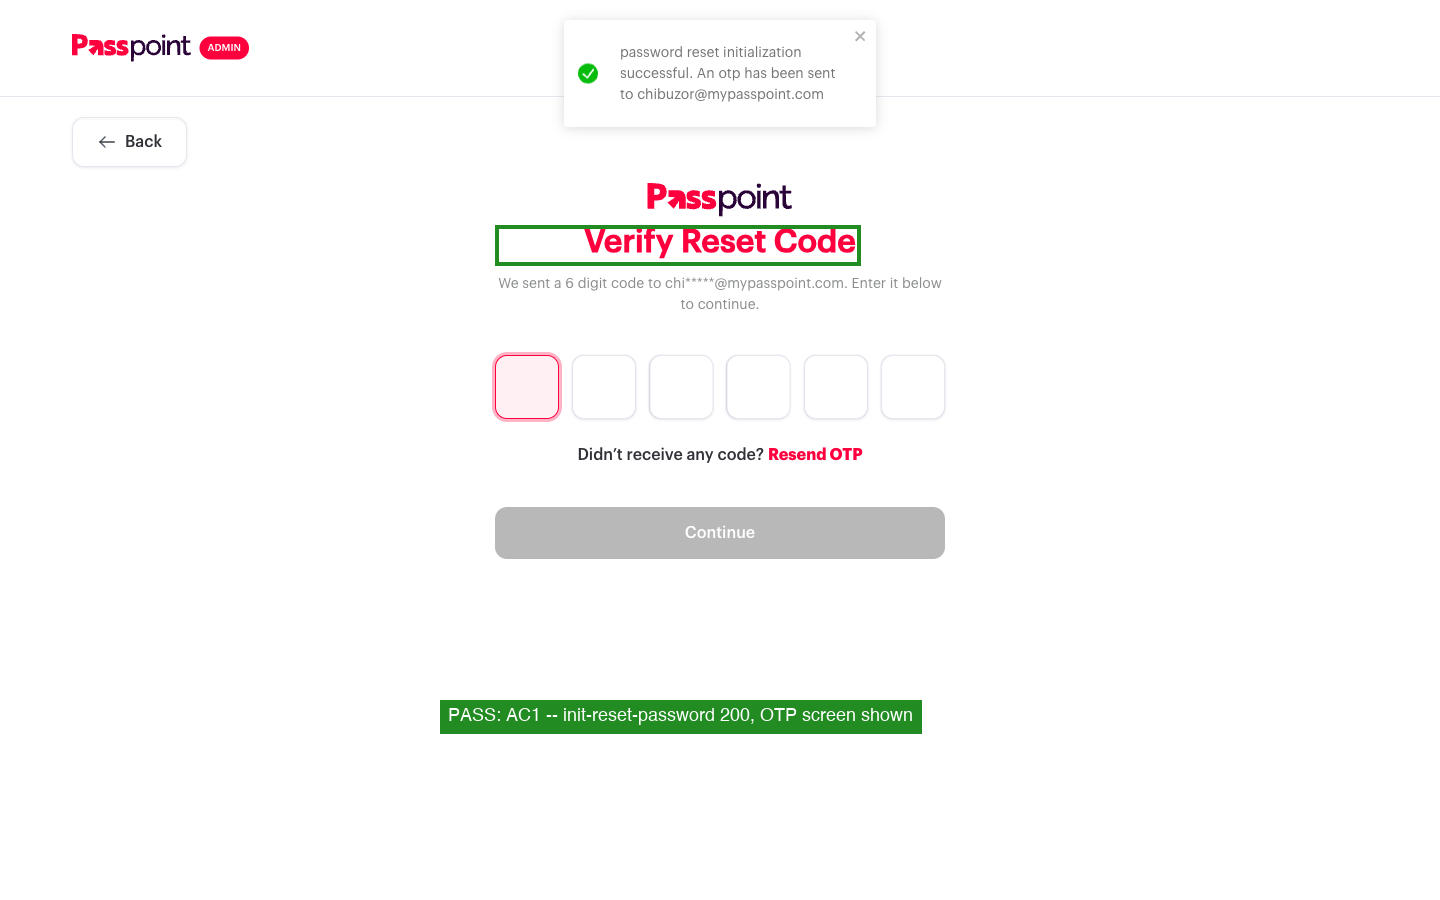
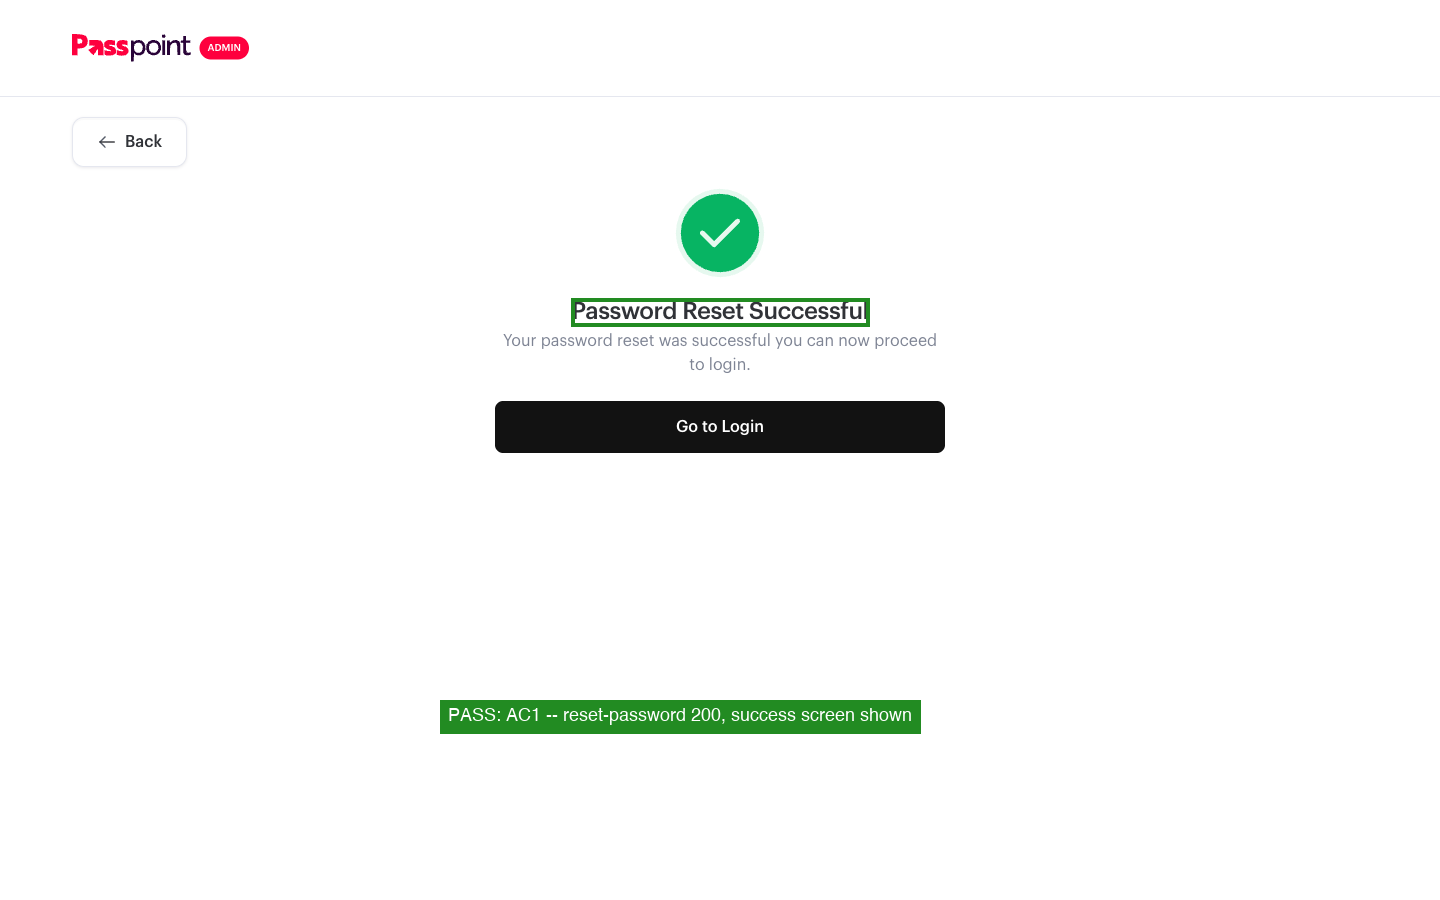
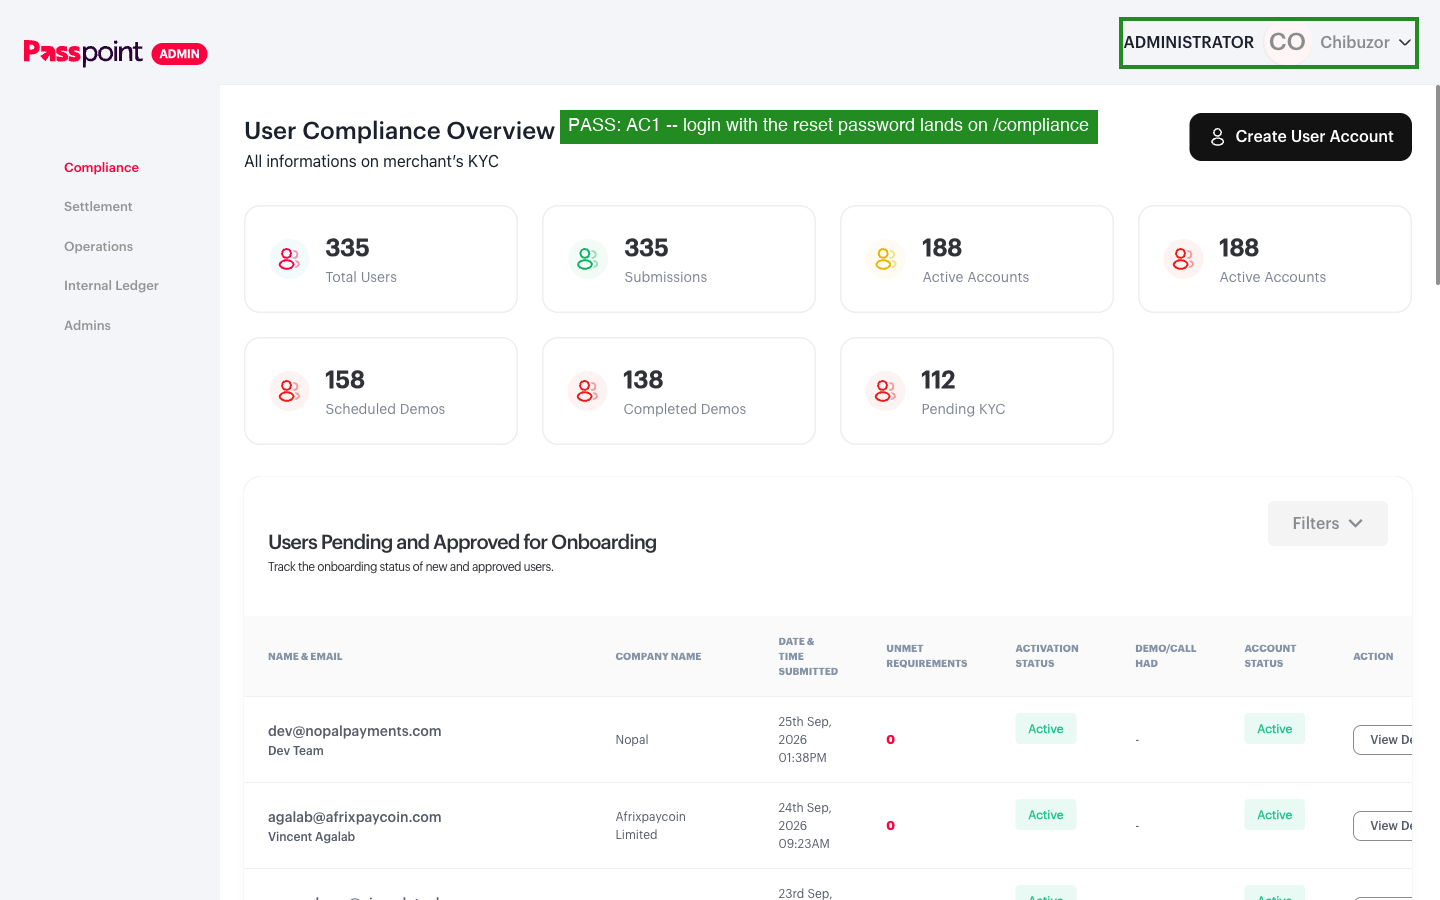
Tested 29 Sep 2026 on admin-sandbox.mypasspoint.com (API: dev.mypasspoint.com/userapp/user-app/), admin account chibuzor@mypasspoint.com. Dev marked ready to test 28 Sep 2026 (Josh Anaba). The reset form rejects the old password "password" (fails 3 of 4 rules), so the account password was changed to a compliant one.
Result summary
| AC | Result |
|---|
| 1. Forgot password end to end (email, OTP, new password, success, login) | ✅ Pass |
| 2. Resend OTP works; expired code returns to email step | ❌ Resend OTP fails (CORS). Expiry / ref 56: ⛔ blocked |
| 3. Wrong OTP stays on OTP screen | ❌ Fail: advances to password step, rejected only on final submit |
| 4. Password policy + confirm match | ✅ Pass |
| 5. Requests hit new user service | ✅ Pass on endpoints/payloads. Merchant comparison not done |
AC2 — Resend OTP FAIL
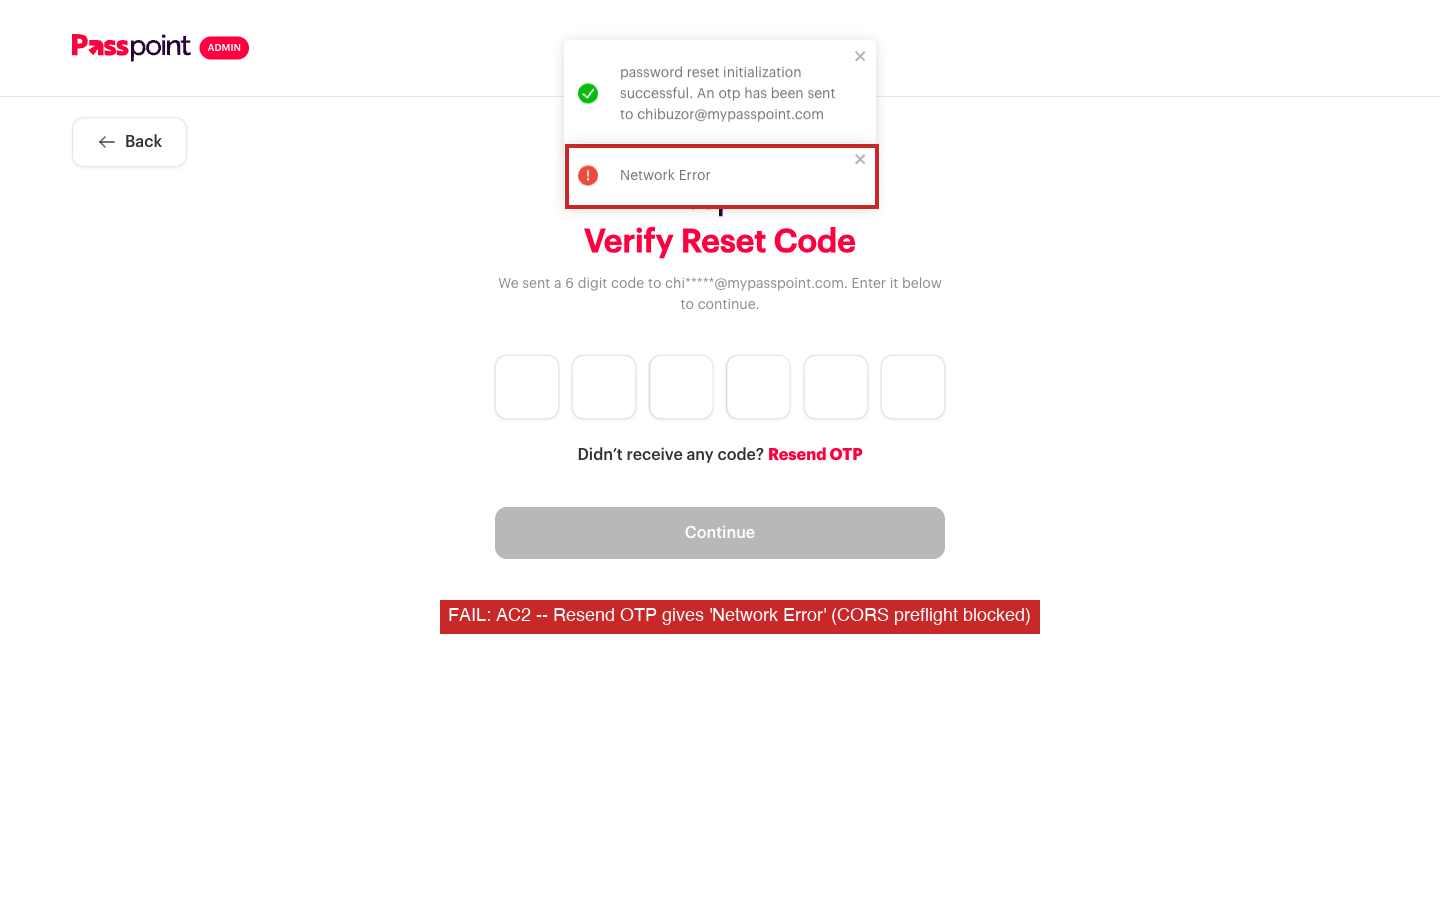
Clicking Resend OTP shows a "Network Error" toast. The browser blocks POST https://dev.mypasspoint.com/userapp/user-app/resend-otp from origin admin-sandbox.mypasspoint.com: "blocked by CORS policy: Response to preflight request" (net::ERR_FAILED). Reproduced on two references. The PUT calls on the same host succeed. Sandbox-only or not is unconfirmed.
BLOCKED Expired code and reference 56 restarting from the email step: not exercised (Resend cannot be used, expiry window unknown).
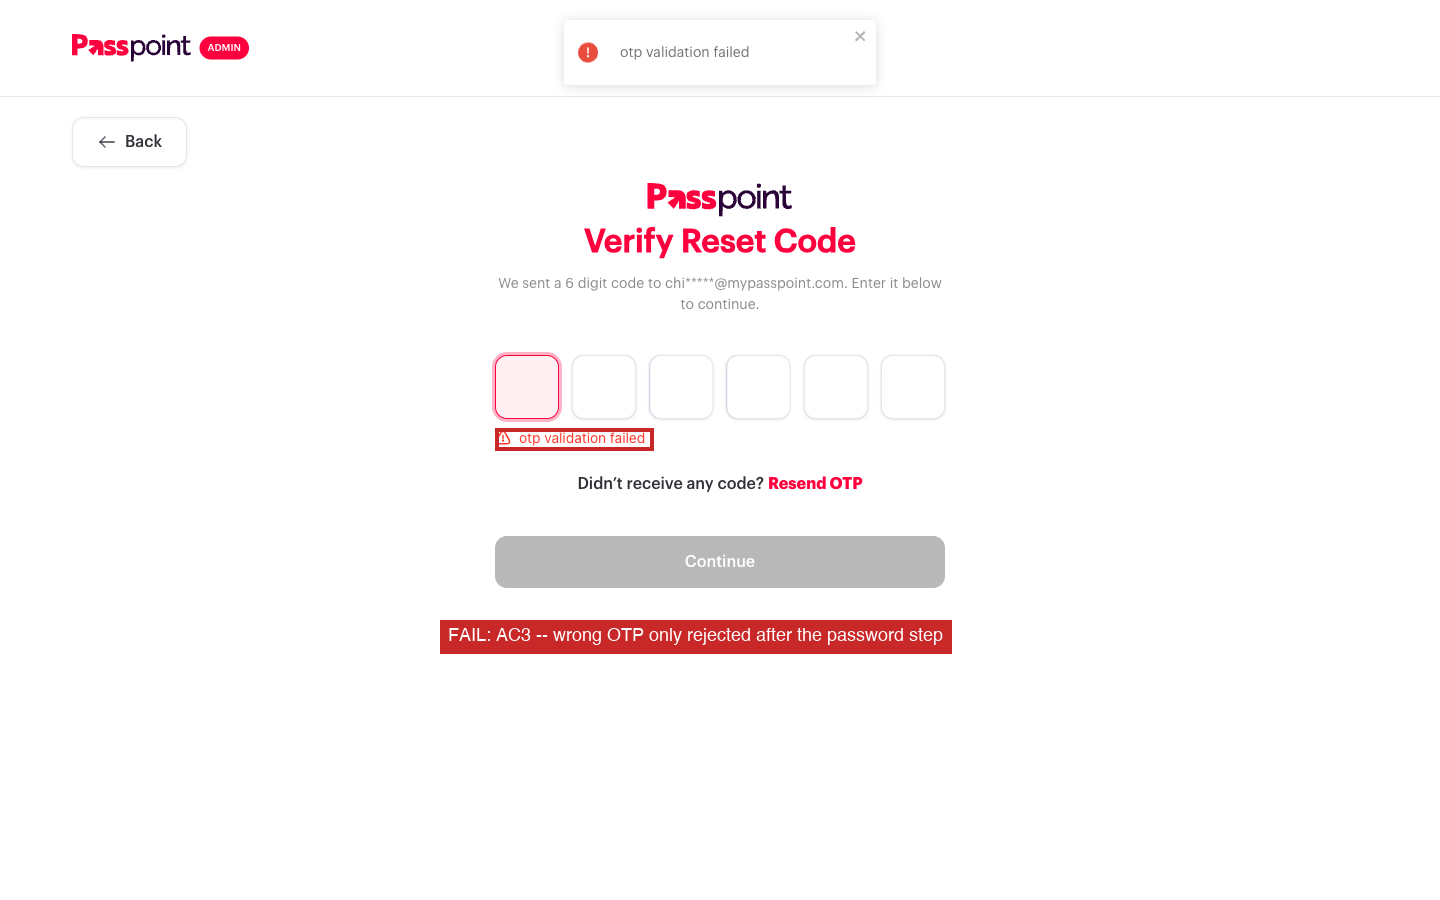
AC3 — Wrong OTP FAIL
Entering 000000 and Continue makes no API call and moves to Create New Password. Only PUT reset-password validates the code: 400 "otp validation failed". The user is then sent back to the OTP screen with the error. Outcome is right, timing is wrong: the wrong OTP does not stay on the OTP screen when entered.
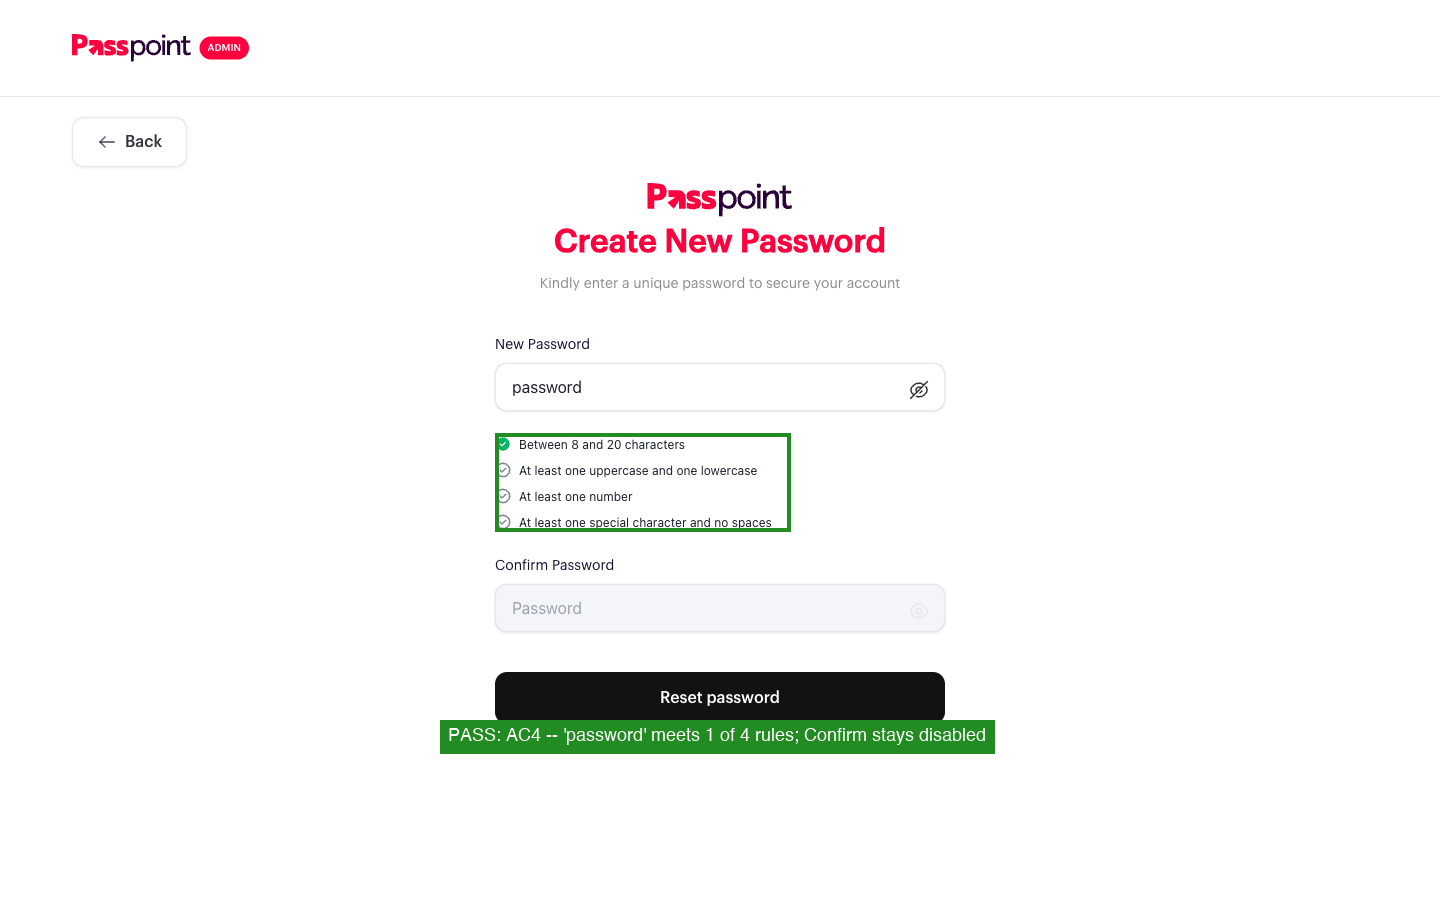
AC4 — Password policy PASS
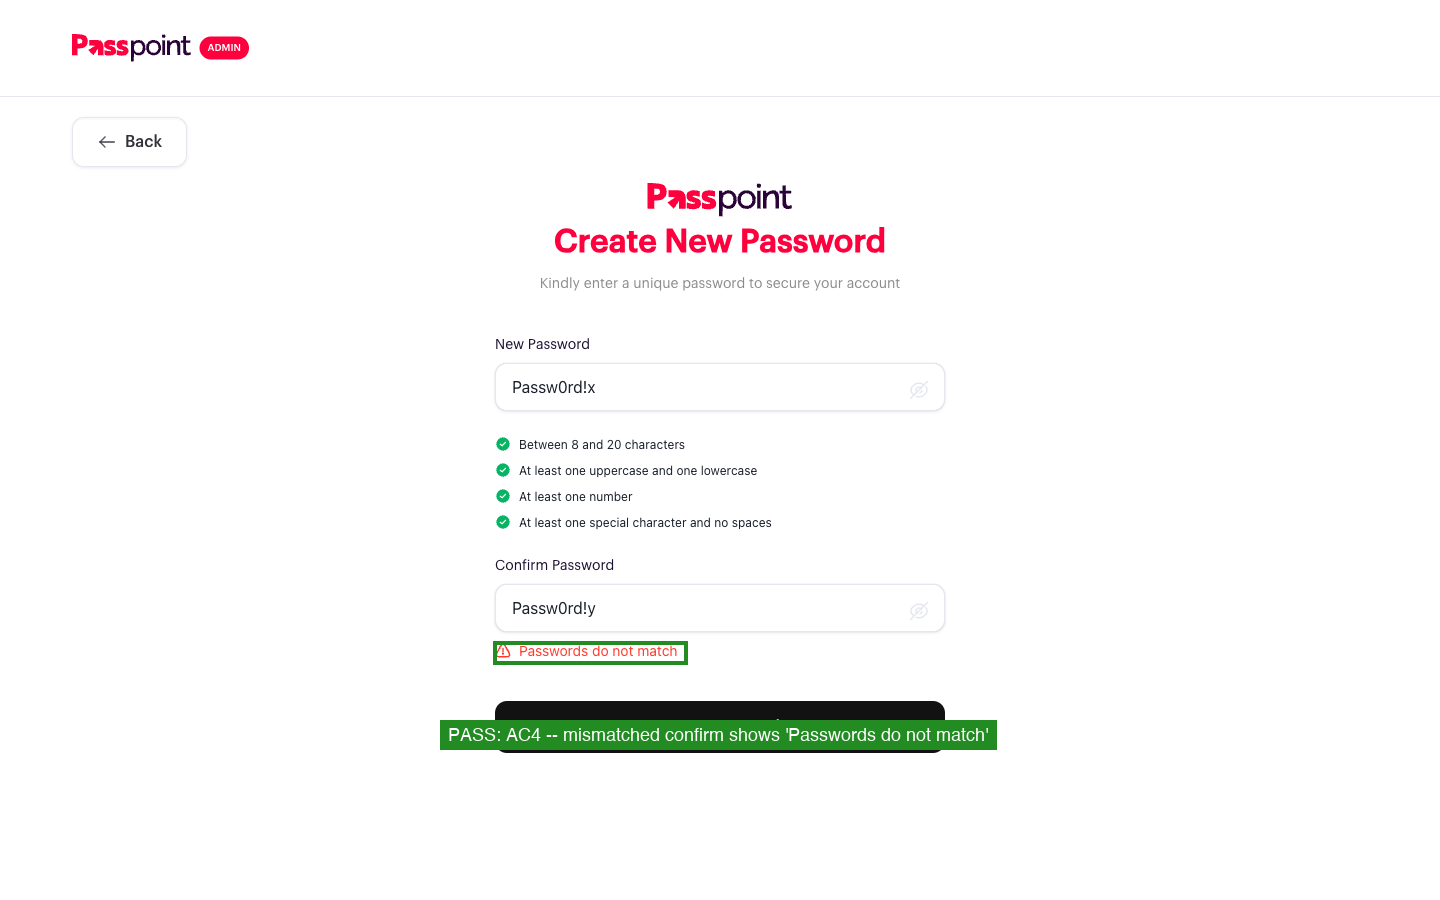
"password" ticks only the length rule; Confirm Password stays disabled. A compliant password ticks all four rules and enables Confirm. A different confirm shows "Passwords do not match".
AC5 — Network contract PASS (partial)
Captured against https://dev.mypasspoint.com/userapp/user-app/:
PUT init-reset-password {"username"} returns reference. POST resend-otp {"reference"}. PUT reset-password {"password","otp","reference"}. Not compared side by side with the merchant Go app.